Continuous pen testing
for SOC 2 compliance
MindFort agents continuously pen test your applications, validate exploitable findings, and keep remediation records ready for security reviews.
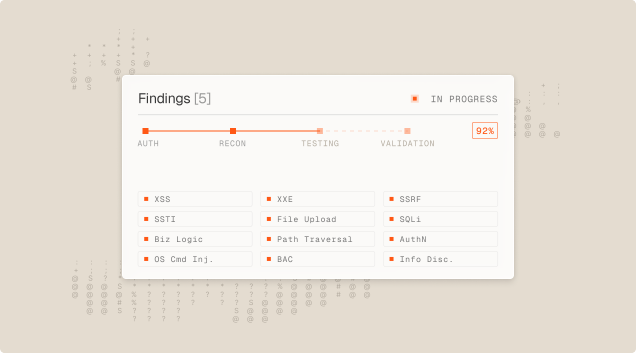
Continuous validation for SOC 2
Agents attack like real adversaries and keep your SOC 2 evidence current.
Control 01
Continuous Testing
Test production-like apps, authenticated workflows, and APIs whenever your controls need fresh evidence.
Control 02
Validate Findings
Agents confirm which findings are exploitable, so your evidence reflects what an attacker could actually reach.
Control 03
Remediation
Pull requests, ticket context, and retest outcomes stay tied to the original finding.
Control 04
Posture Reports
Share audit-ready summaries with control owners, auditors, customers, and partners.
Identify SOC 2 blockers faster.
Continuous testing and remediation records that support SOC 2 control operation.
Configure agents
Scope agents to approved targets, set rate limits, and document validation for security controls.
Auditor-ready reports
Clear exports that show what was tested, what was found, and what was fixed.
Continuous coverage
Scheduled and release-triggered assessments keep evidence aligned with your current application.
Frequently
Asked Questions
Common questions about SOC 2 evidence with MindFort.
No. MindFort helps you operate and document security testing controls. Your auditor still evaluates your SOC 2 program and evidence.
Yes. Reports can include assessment scope, validated findings, remediation status, retest results, and supporting activity logs.
Yes. Teams can run an assessment before reviews, renewals, or procurement requests to share fresh proof of security work.
Agents validate every finding with a working exploit, so false positives stay under 1%, and they retest fixes so teams can show clear closure.