Run custom security engineering tasks
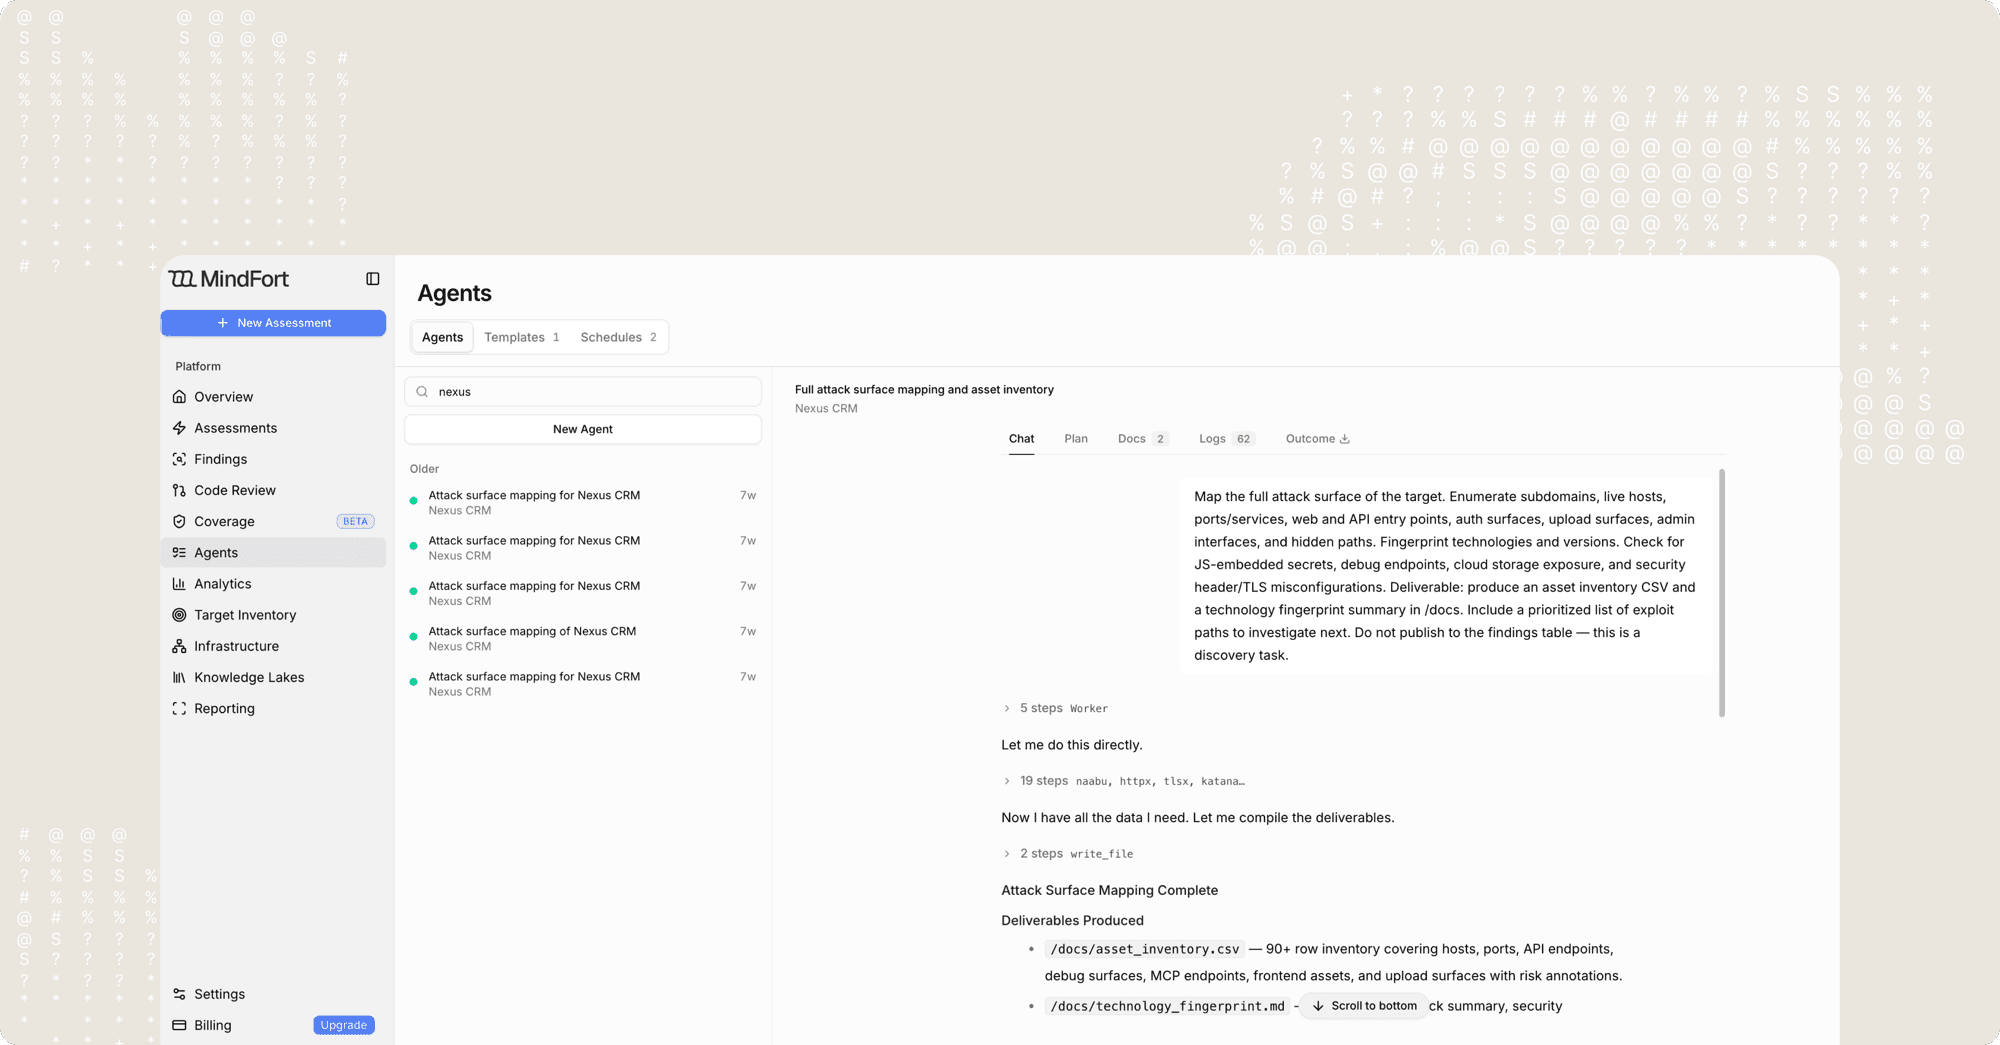
Describe the task in plain language. Agents plan it, execute it against your targets, and report back with evidence.





How it works
The same agents that pen test your apps will run whatever you point them at.
Connect MindFort to your workspace
Add MindFort to Slack, then @-mention it wherever your team already works to kick off a task.
Agents plan and execute
Agents break the task into steps, run it against your scoped targets, and adapt when something unexpected comes back.
Get a report back
Findings come back documented, with severity, evidence, and the steps that produced each one.
Agentic Control System
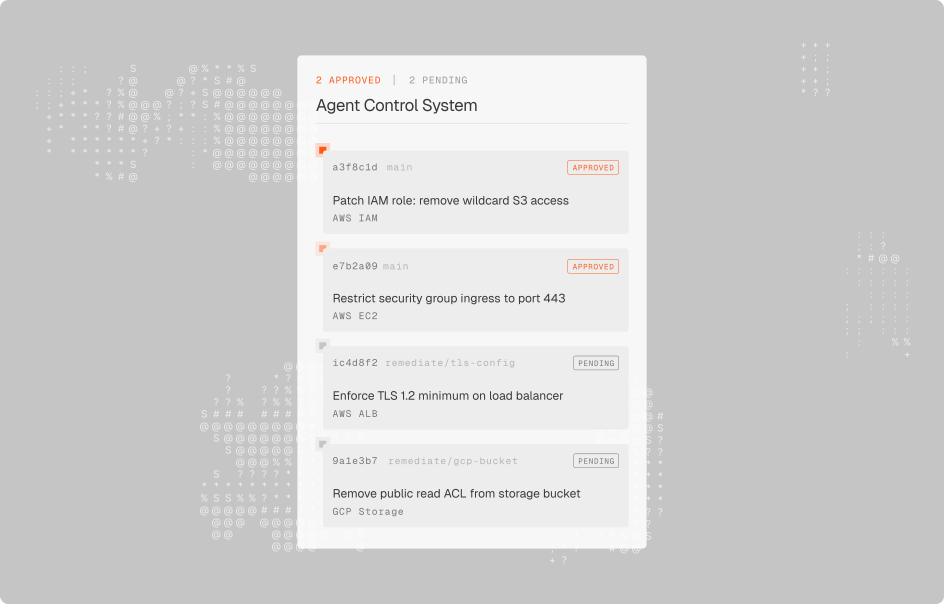
Agents fix more than code. When they change cloud configs, network policies, or infrastructure, the Agentic Control System records every change, routes it through approval, and lets you roll it back. Think git, for everything that is not code.
Version control
Every agent-made change is versioned with full before/after state, so you always know what changed and can roll back.
Approval workflows
Route changes through your existing approval process. Agents propose, your team approves, agents apply.
Full audit trail
A complete history of every remediation: who, what, when, and why. Built for compliance.
Speed with control
Agents move fast. The control system means they never move faster than your visibility.
Agent First
MCP native by default, persistent memory across runs, and a control surface designed for steering agents instead of configuring scanners.
MCP native by default
Agents discover and call tools through the Model Context Protocol, so your scanners, code hosts, ticketing, and cloud APIs plug in without glue code. Add a new MCP server and agents start using it on the next run.
Built to run continuously
Trigger on every CI/CD push, on a schedule, or always on. Agents probe, adapt, and remember what worked across operations instead of starting from scratch every time.