

Offensive security swarms.
AI agents that attack your live applications in parallel, prove exploitable vulnerabilities, and help you fix them at scale.






See where an attacker can get through.
MindFort attacks your running application through its real interfaces, testing authentication, permissions, and deployed defenses together.
Legacy solutions
Agentic code scanning, DAST, human-assisted AI pen testing
- Potential issues to triage
- Deployment context incomplete
- Exploitability unconfirmed
MindFort
- Impact proven in the live app
- Reproduction evidence attached
- Original attack retested after the fix
An AI red team for your live applications
Hack your live running applications
Agents attack the running application the way an attacker would, and when you connect the repo, they trace each finding back to the code that caused it.
Results in hours
Verified findings, not a PDF six weeks later.
- Time to verified findings
- < 8 hrs
- to verified findings
- Time to first deployment
- < 10 min
- to first deployment
Traditional pentests: 2-6 weeks
Highly scalable testing
Thousands of agents run in parallel. Coverage scales with your attack surface, not your headcount.
Full MCP & integrations
Start tests from CI/CD, push findings to your tracker, and drive agents through our API and MCP.
- GitHub
- Linear
- Jira
- Slack
Validated findings
Agents validate every finding with a working exploit.
- False positive rate
- < 1%
- false positives
- Findings with proof of exploit
- 100%
- with proof of exploit
Every finding ships with steps to reproduce
Each attack teaches the next.
Agents build on what they learn about your application, its permissions, and its defenses. Each run starts with that context.
MindFort’s performance across internal benchmarks (2026)
From attack to verified fix.
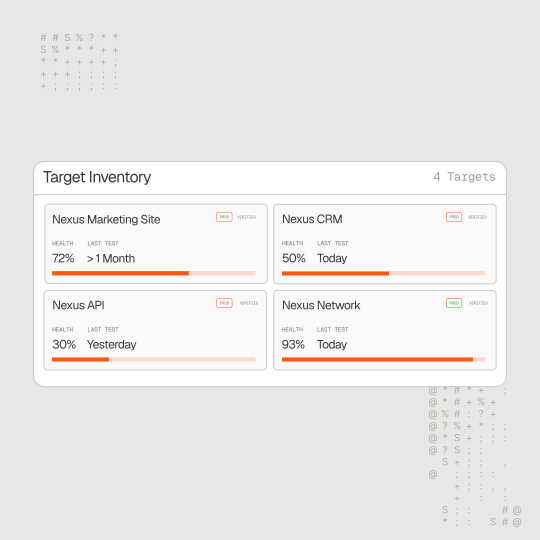
Test the live application
Give the AI red team your apps, APIs, and test accounts. Agents explore how your application works and test its defenses.
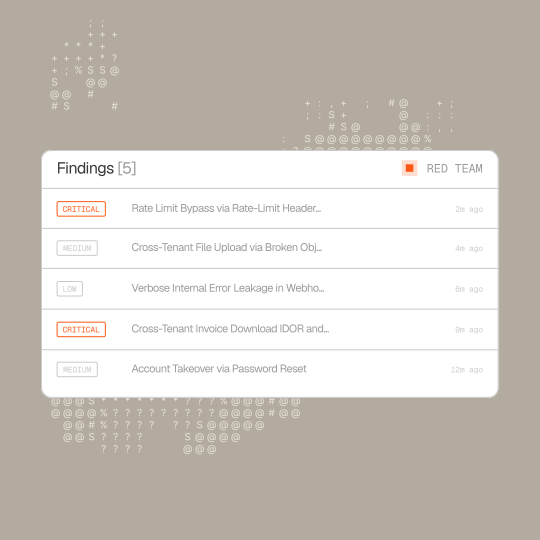
Prove the finding
Agents confirm what an attacker can access or change. Every finding includes a working exploit and steps to reproduce it.
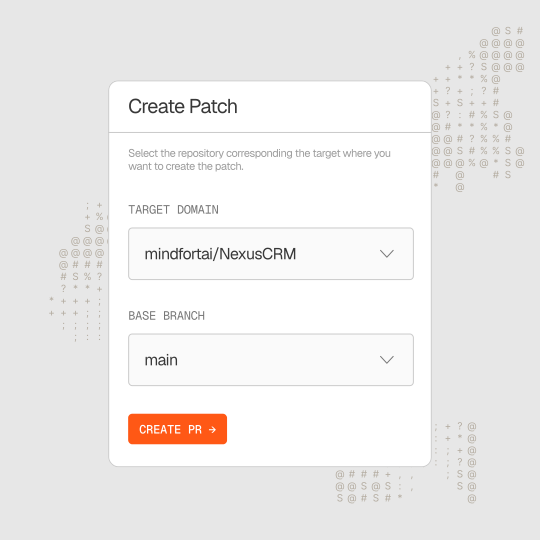
Verify the fix
The AI engineering team opens a patch pull request. After deployment, MindFort repeats the attack to check that the fix holds.
Keep testing as you ship.
New features create new ways in. Run recurring pen tests to find exploitable changes and verify deployed fixes.
First Results
Hours
Coverage
24/7
False Positives
<1%
Setup
Minutes