Generate audit-ready reports
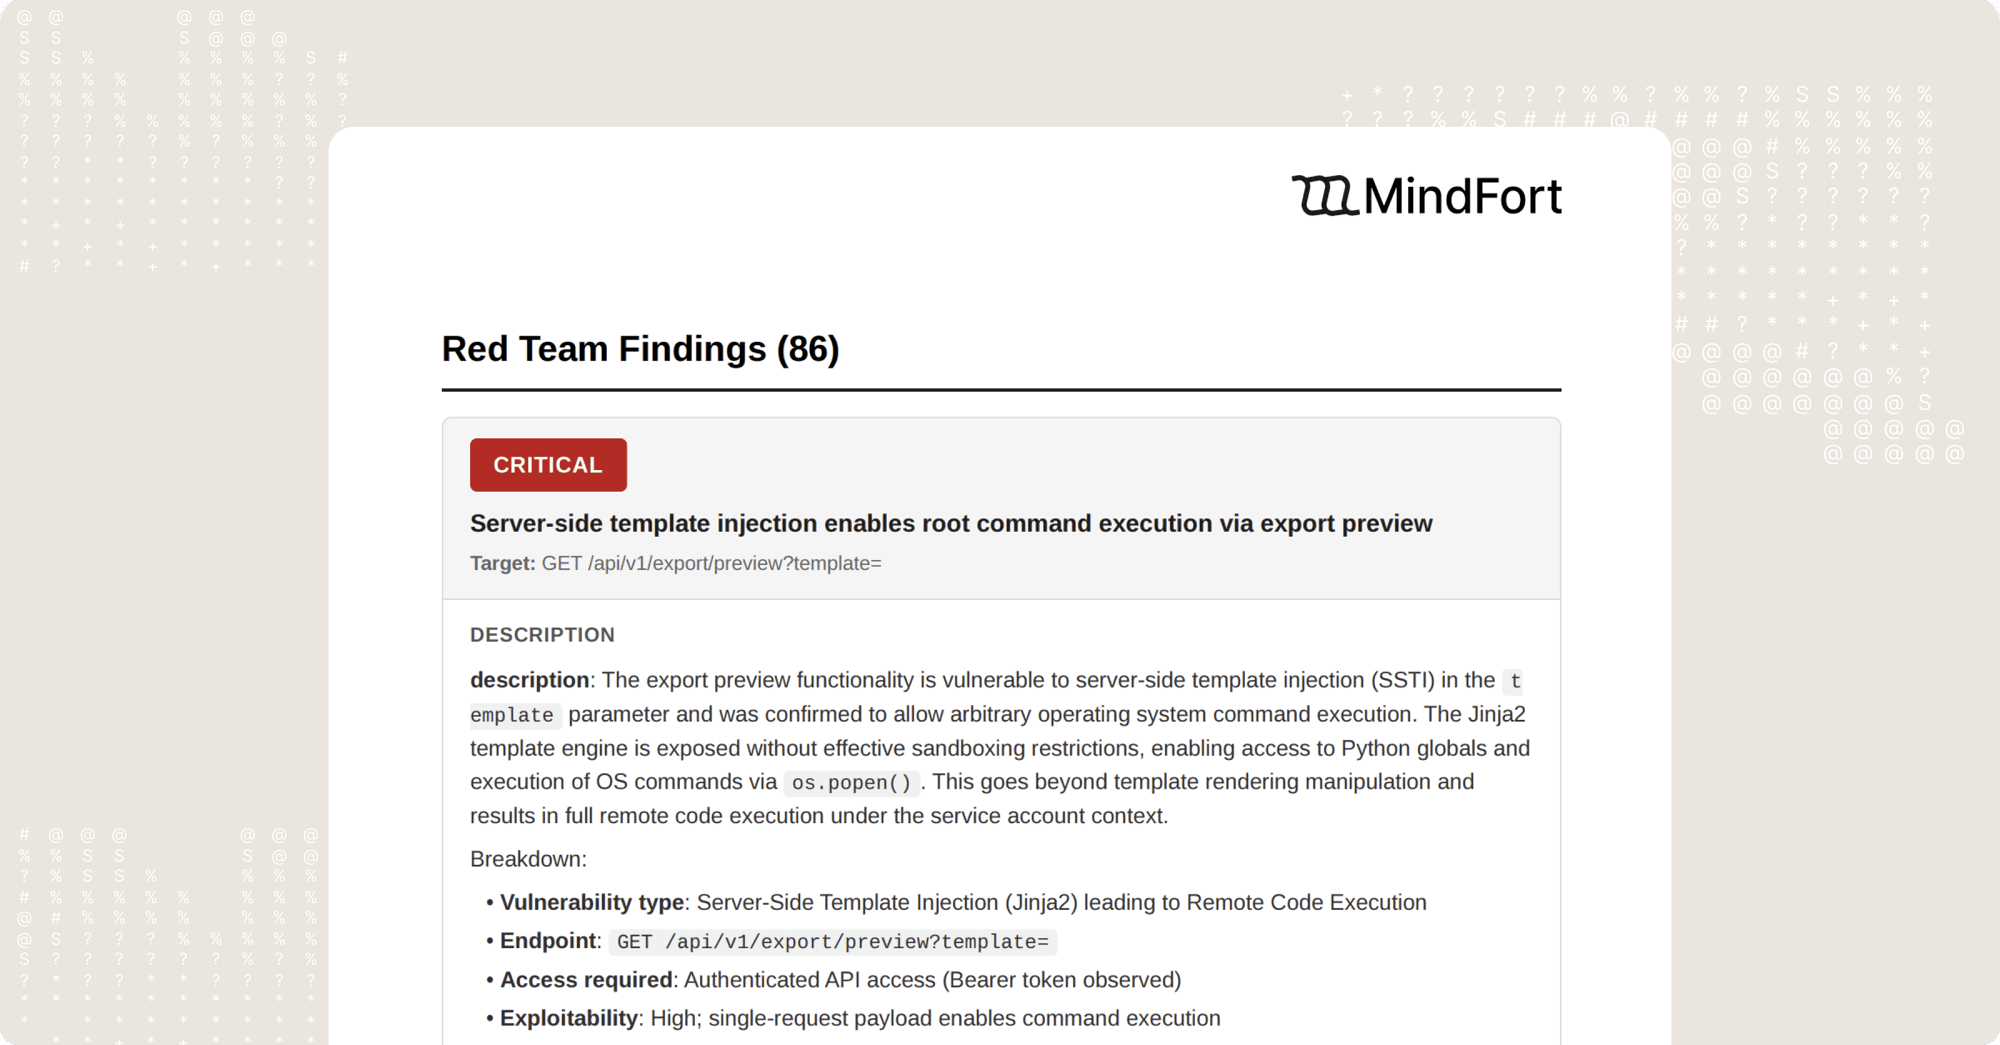
Every agent action is logged and every finding documented, so pen test reports and audit evidence are ready before anyone asks.





How it works
Every report is a byproduct of work the agents already did.
Document vulnerabilities as agents work
Every request, response, and exploit attempt behind a finding is logged with full context. Nothing to reconstruct later.
Generate the report automatically
Findings, severity, methodology, and remediation status assemble into a pen test report with no manual write-up.
Export where it's needed
Share with auditors, attach to security questionnaires, or push into Jira and Linear with full detail intact.
Agentic Control System
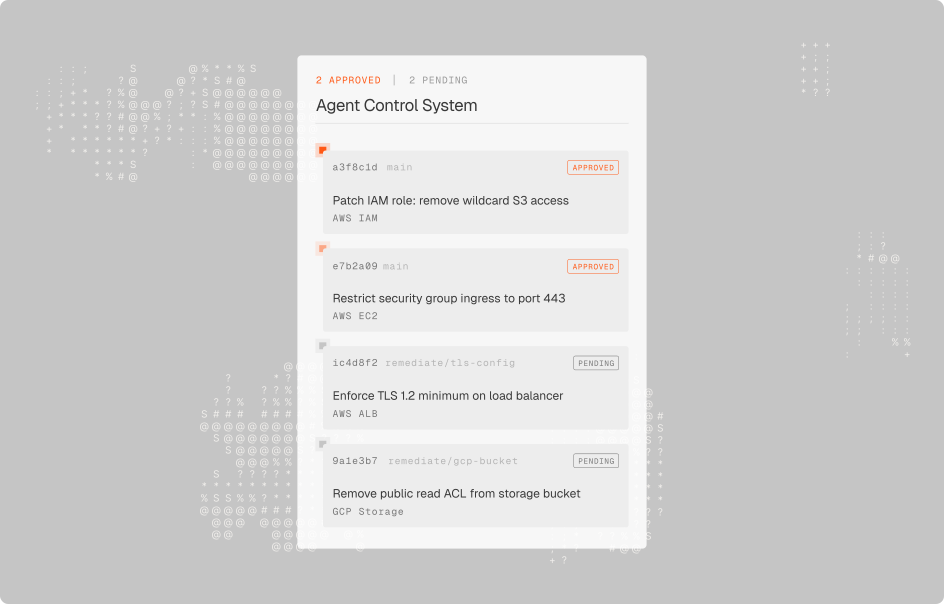
Agents fix more than code. When they change cloud configs, network policies, or infrastructure, the Agentic Control System records every change, routes it through approval, and lets you roll it back. Think git, for everything that is not code.
Version control
Every agent-made change is versioned with full before/after state, so you always know what changed and can roll back.
Approval workflows
Route changes through your existing approval process. Agents propose, your team approves, agents apply.
Full audit trail
A complete history of every remediation: who, what, when, and why. Built for compliance.
Speed with control
Agents move fast. The control system means they never move faster than your visibility.
One platform replaces the scanner stack
Agents run every capability below as part of every operation. Nothing separate to buy, configure, or monitor.
Penetration testing
End-to-end pen tests against your live environment with compliant, exportable reports.
Dynamic application security
Agents perform deep DAST analysis natively, with no separate scanner. Authenticated crawling, business logic testing, and API security in every run.
Vulnerability management
Findings are validated, deduplicated, risk-scored, and tracked over time. Agents triage so your team doesn't have to.
Software composition analysis
Agents identify vulnerable dependencies and open-source risks across your codebase as part of every operation.
Threat intelligence
Agents draw on real-time threat data to prioritize what matters, testing for actively exploited CVEs and emerging attack techniques.
Attack surface mapping
Continuous discovery and monitoring of every exposed asset across your organization: subdomains, APIs, cloud resources, and more.