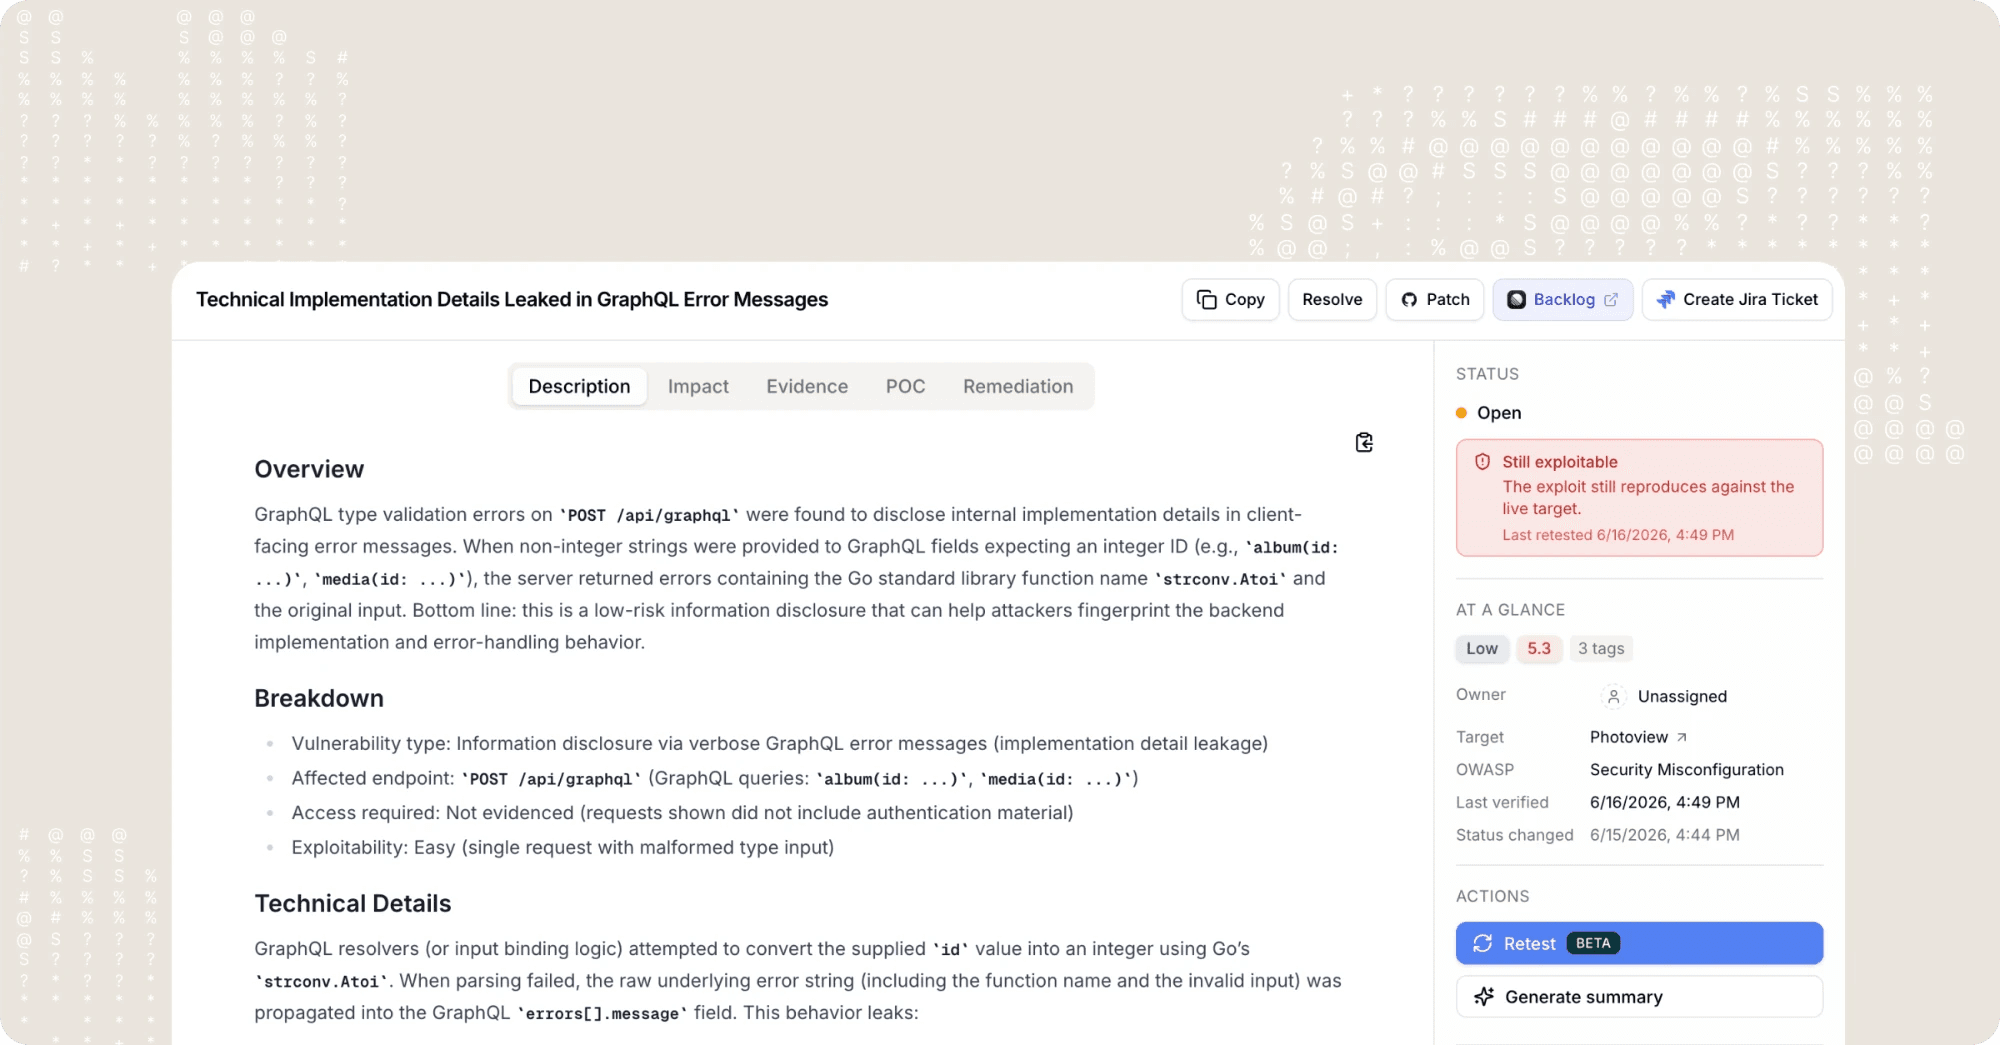
Validate and prioritize every finding
Agents confirm, deduplicate, and risk-score every result so your team only sees what's real and what matters.






How it works
From raw findings to a ranked, deduplicated queue, automatically.
See real vulnerabilities
Agents confirm each finding with a working exploit, so the queue is never noise.
Classify by real-world severity
Findings carry a CVSS 3.1 base score plus a severity scored on exploitability and business context in your environment.
Get merge-ready fixes
Each confirmed finding comes with a verified patch, ready to merge.
One platform replaces the scanner stack
Agents run every capability below as part of every operation. Nothing separate to buy, configure, or monitor.
Penetration testing
End-to-end pen tests against your live environment with compliant, exportable reports.
Dynamic application security
Agents perform deep DAST analysis natively, with no separate scanner. Authenticated crawling, business logic testing, and API security in every run.
Vulnerability management
Findings are validated, deduplicated, risk-scored, and tracked over time. Agents triage so your team doesn't have to.
Software composition analysis
Agents identify vulnerable dependencies and open-source risks across your codebase as part of every operation.
Threat intelligence
Agents draw on real-time threat data to prioritize what matters, testing for actively exploited CVEs and emerging attack techniques.
Attack surface mapping
Continuous discovery and monitoring of every exposed asset across your organization: subdomains, APIs, cloud resources, and more.