Pen test your live apps, continuously
AI agents probe your production apps and APIs around the clock, finding and confirming real exploits before attackers do.





How it works
Set a schedule, find real vulnerabilities, and fix them. Zero manual effort.
Schedule a pen test
Pick a target, set the frequency, and choose your depth. Agents handle the rest.
Find real vulnerabilities
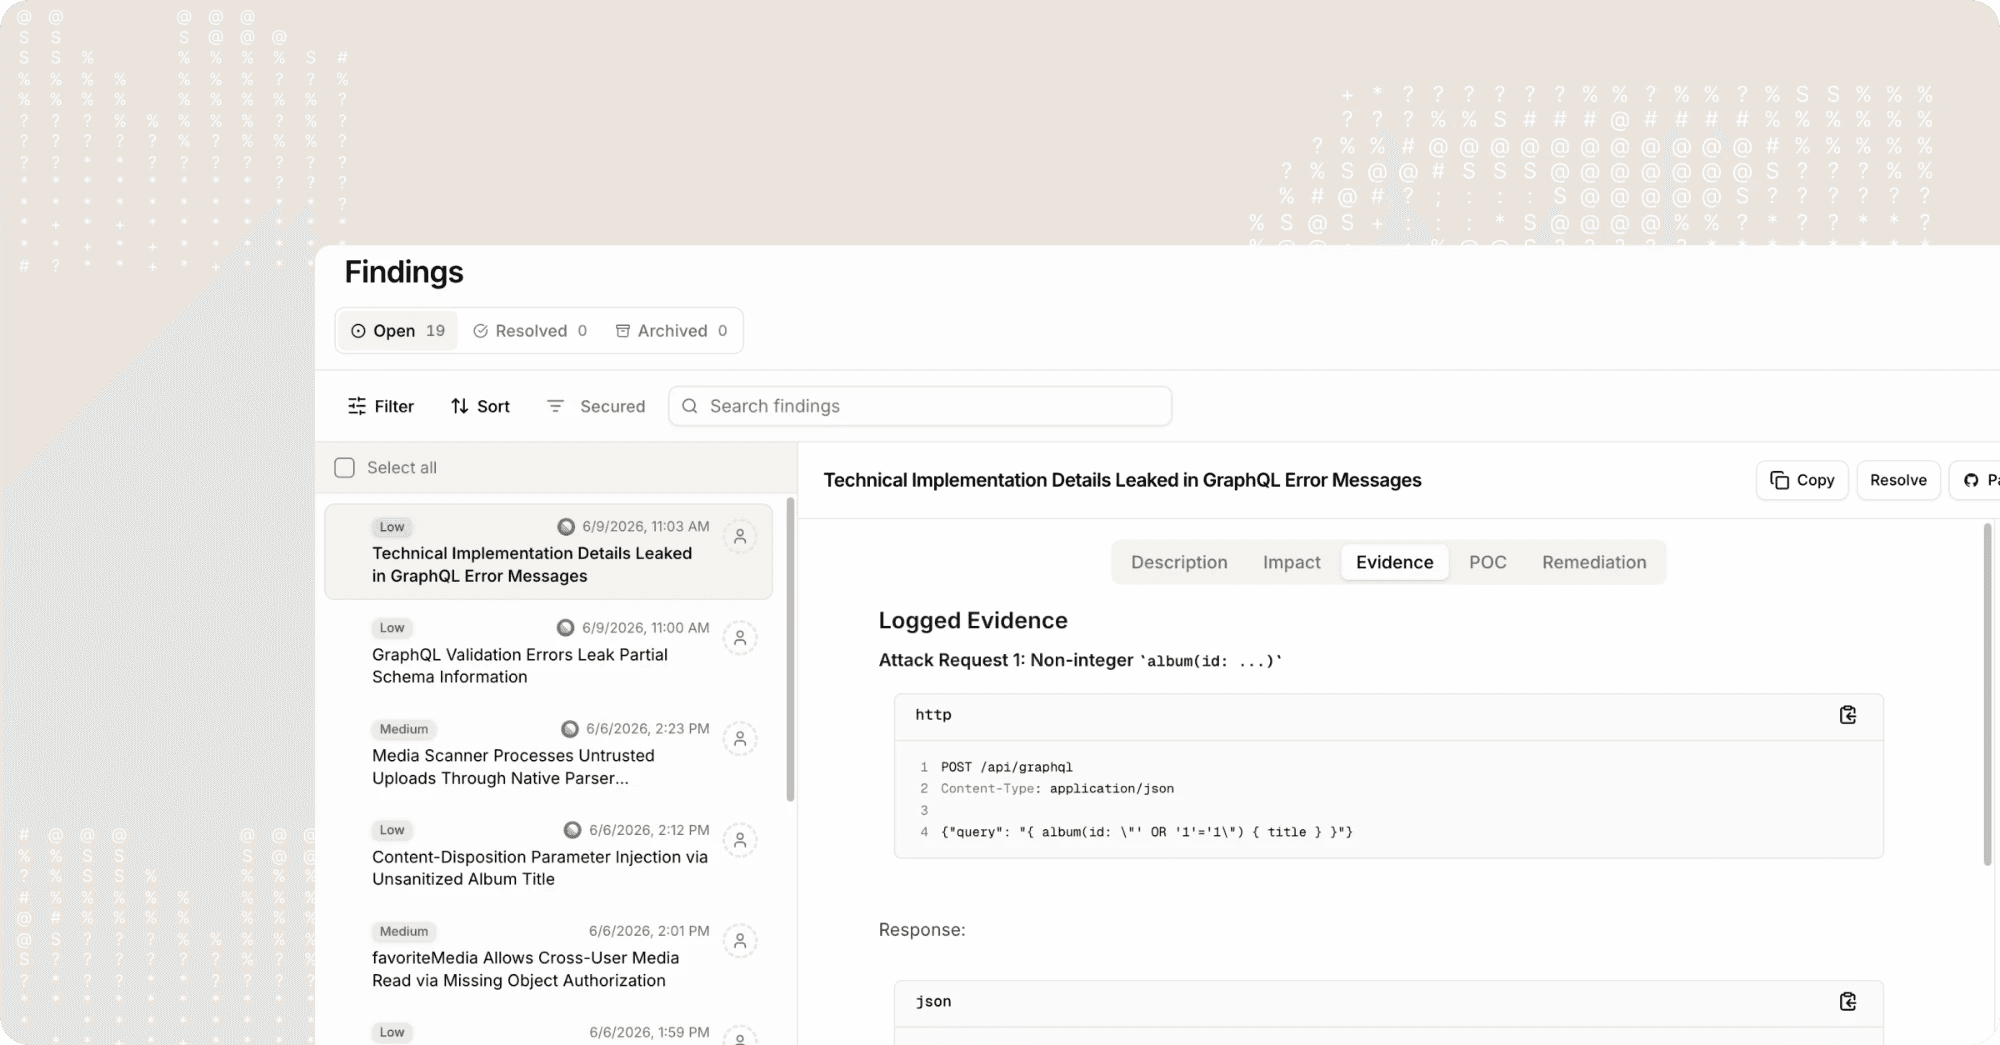
Agents probe your apps, APIs, and infrastructure the way an attacker would.
Get merge-ready fixes
Each finding comes with a verified patch, delivered as a PR you can merge.
Two Ways to Deploy
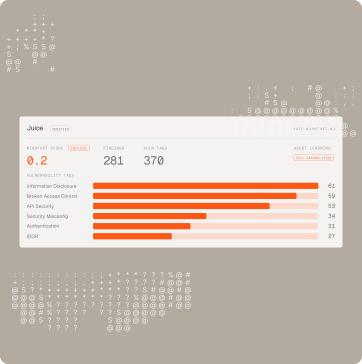
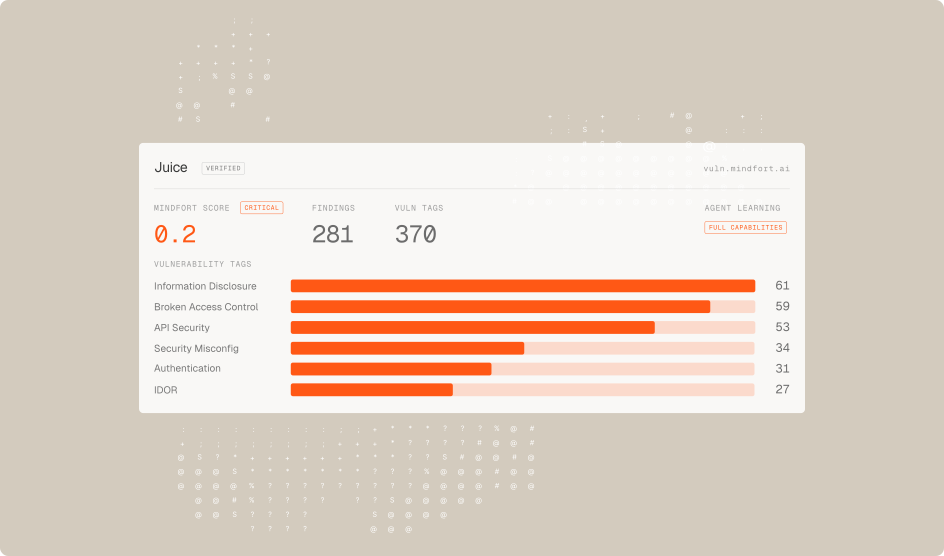
Black Box
Agents attack with no knowledge of your codebase, exactly like an external attacker.
Schedule on demand, weekly, or monthly. First results in hours.
White Box
Agents also read your source code, so they can trace data flows, spot logic flaws, and find more in every run.
Schedule on demand, weekly, or monthly. First results in hours.
Security that gets better the longer it runs
Agents never start from scratch. They remember your stack, your deploy patterns, and your defenses, so every run starts smarter than the last.
Environment-aware testing
Agents map how your teams build, deploy, and configure systems, tailoring their testing and remediation to your specific stack and conventions.
Continuous context building
Every operation deepens an agent’s understanding of your environment. Past findings, infrastructure changes, and deployment patterns all inform future runs.
Adaptive attack strategies
Agents remember what worked and what didn’t. They evolve their approach based on your specific defenses, getting sharper with every cycle.
Efficient at scale
Agents skip re-discovering what they already know. That time goes into deeper testing and broader coverage.